What to know
- Dependencies and build tools are part of the delivered system’s trust chain.
- Provenance and inventories answer different questions from vulnerability scans.
- A signed artifact or lockfile is useful evidence, not a complete security guarantee.
The meaning
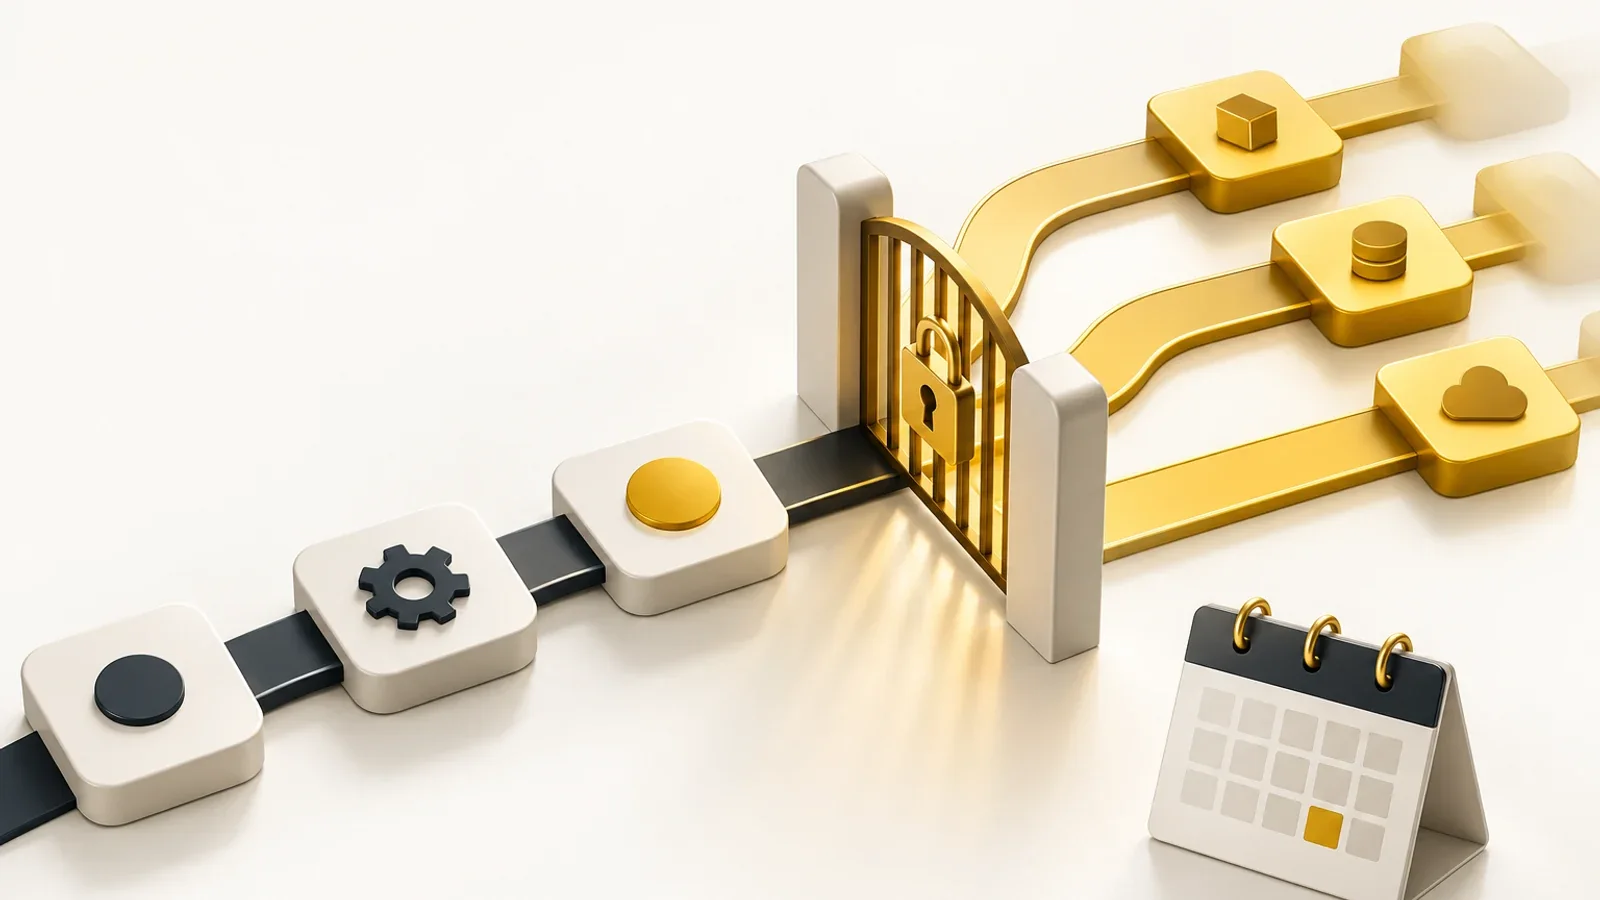
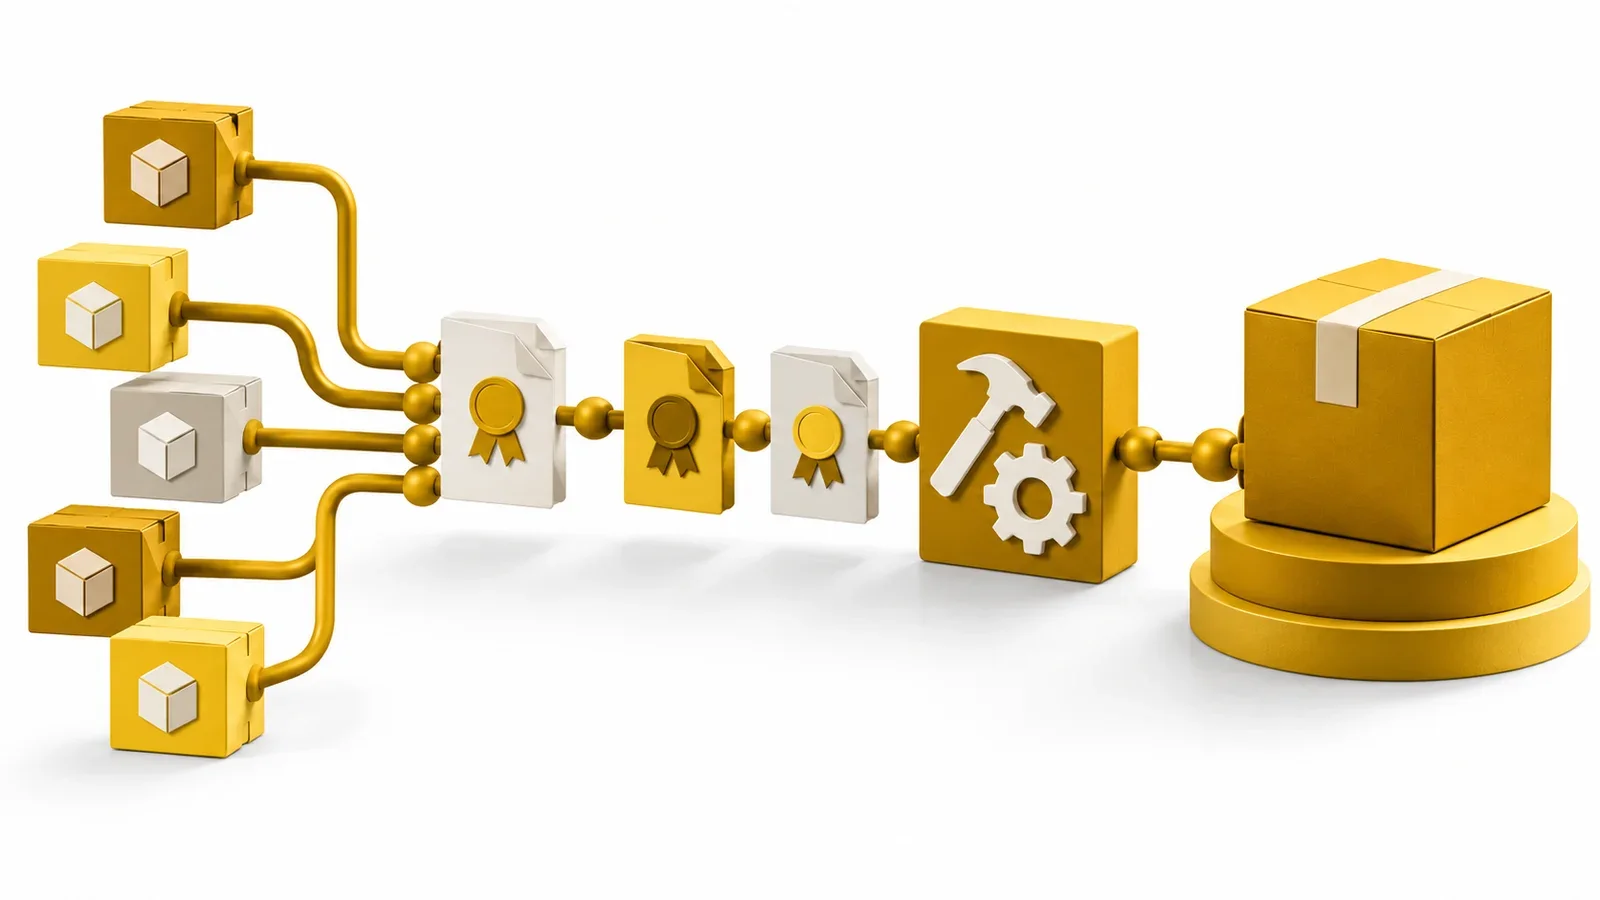
A software supply chain is the set of people, components, tools and processes involved in producing and delivering software. It includes more than the source repository: dependencies, package registries, build environments, signing processes and distribution channels can all influence what reaches a user. NIST’s broader supply-chain definition and Secure Software Development Framework support examining development and delivery together. The useful question is where code or authority can enter the path to the final application.
Why a dependency list is incomplete
A package inventory can show included components, while a build record can show which tools transformed them. A lockfile can improve reproducibility without proving a package is benign. A vulnerability scan can identify known findings without establishing that every input was authentic or that a release was built from the reviewed revision. These forms of evidence complement one another. Treating one green result as the whole assessment hides the separate questions it never attempted to answer.
A publication example
Imagine a site whose image processor depends on a native library and whose build script downloads an additional tool. Reviewing only the article templates misses both inputs. A practical inventory would identify the processor version, the downloaded artifact’s source and integrity check, and the build identity allowed to publish. The example is hypothetical; it does not allege a flaw in a named package. It shows why execution during installation deserves the same attention as execution after deployment.
What useful controls aim to preserve
A team can restrict who changes dependencies, retain provenance for release inputs and verify the artifact actually distributed. It also needs a way to respond when a component is later found vulnerable. Signing can help establish an artifact’s origin under a particular key; it does not prove the artifact’s behavior is correct. The term is useful because it expands responsibility beyond writing application code while keeping each evidence claim precise. A manageable supply chain is one whose important inputs, authority and recovery steps can be explained.
References
- NIST supply-chain glossary (living reference; accessed 2026-10-16)
- NIST Secure Software Development Framework (living reference; accessed 2026-10-16)
Editorial note: AI-assisted original educational definition reviewed 16 October 2026. Examples and reading questions are BijliCoin explanation, not a product recommendation, legal conclusion or guarantee. AI-generated conceptual illustration.
Sources & context
See our editorial policy or report a correction.
Related guides and definitions
- A database backup needs a restore rehearsal to become useful evidence
A practical guide to defining recoverable data, rehearsing restoration safely and distinguishing a backup file from a recovery capability.
- Make a publication faster without breaking the reading path
A practical performance review for article sites that treats reading, forms and accessibility as outcomes to preserve.
Join the conversation.
Loading reader discussion…
Sign in to like this article or add a comment. Comments are reviewed before appearing publicly.
Open the sign-in link in this same browser. Your display name is public; your email is private. Reader sign-in does not subscribe you to the newsletter. See our privacy notice.
Signed in as