What to know
- A proposal from a model is not authority to act.
- Validate tool name, arguments, caller and resource scope.
- Enforce consequential permissions outside the model’s narrative.
The working definition
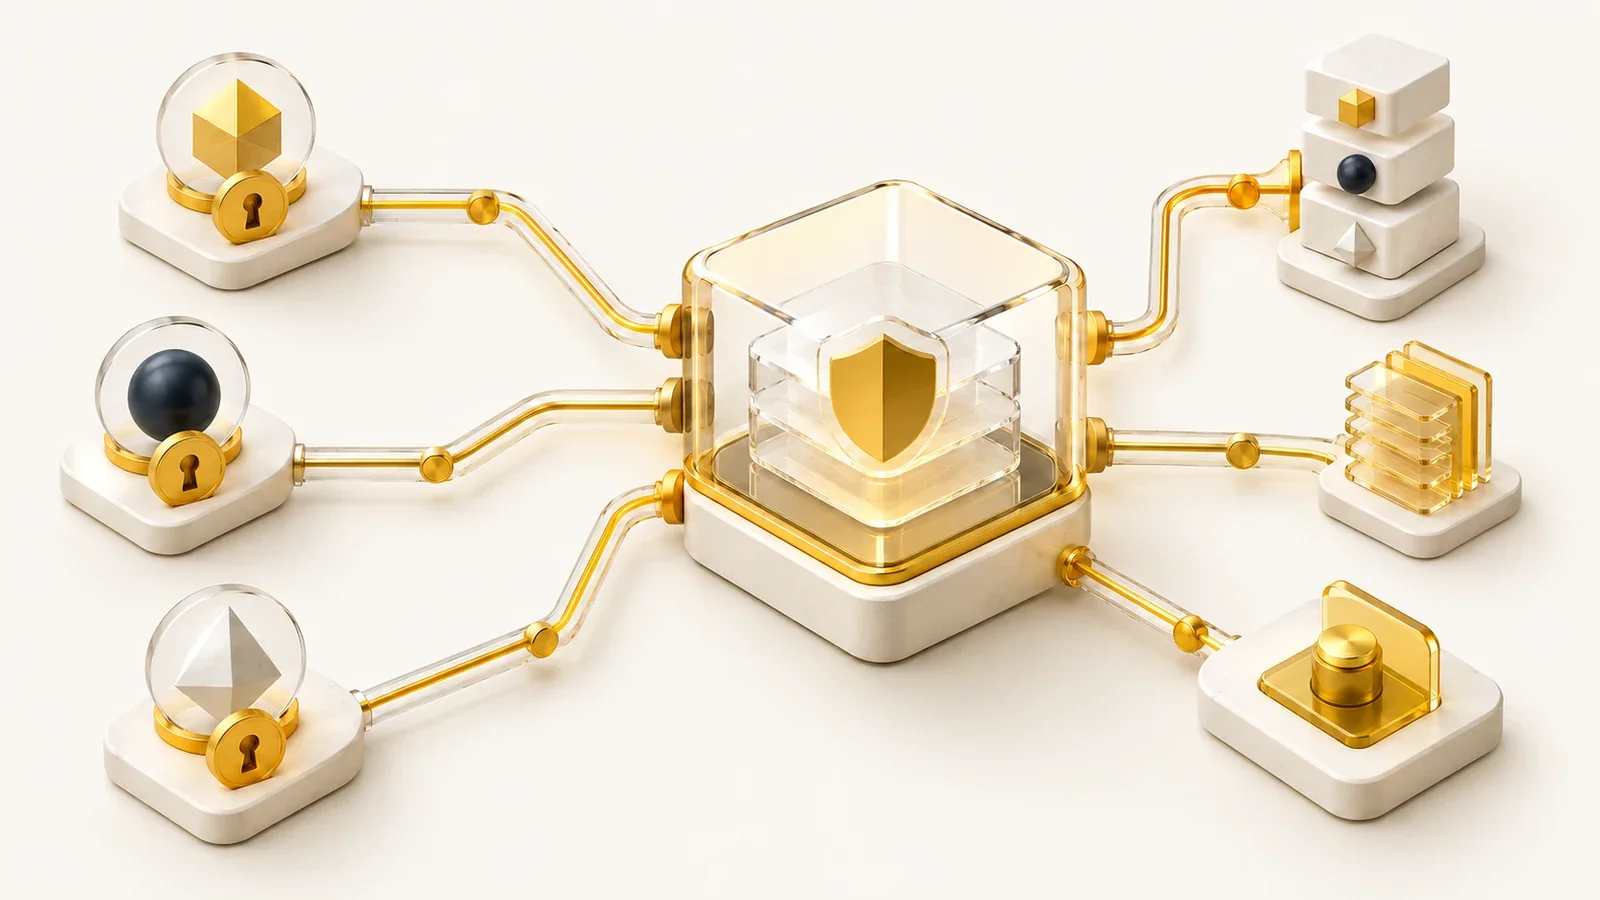
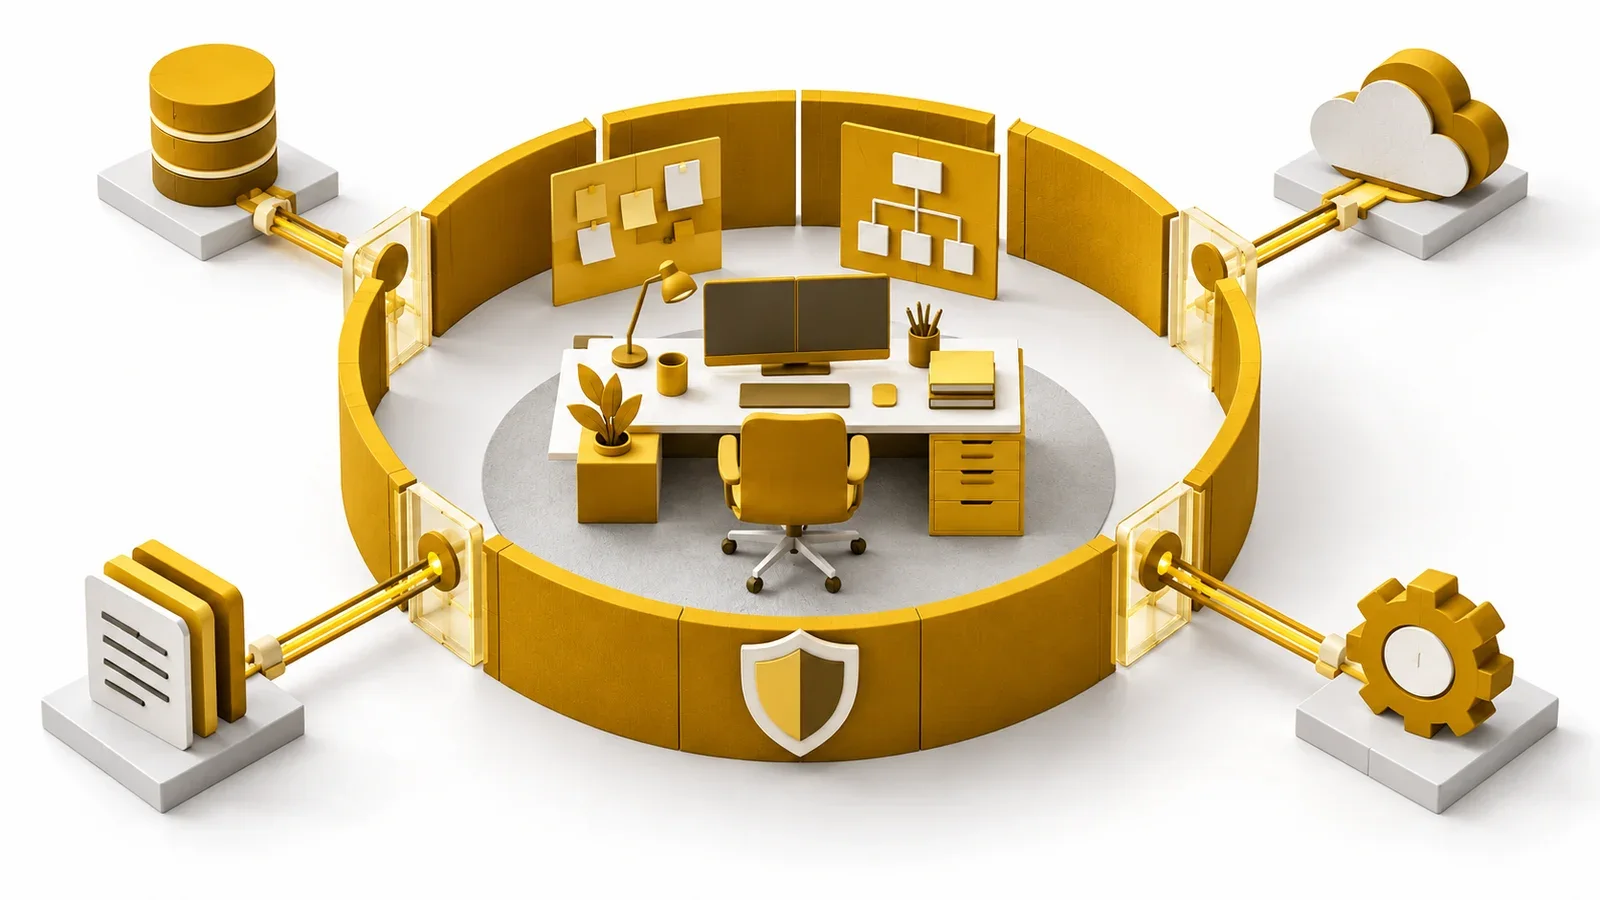
An agent tool boundary is the separation between a model proposing an operation and a tool being allowed to perform it. This is a practical engineering term rather than a claim of a single formal standard with that title. The boundary includes which tools exist, what arguments they accept, which identity calls them and which resources that identity may affect. A convincing explanation generated by a model does not replace those checks.
Why the boundary matters
An assistant may read a web page while holding access to another system. The page can provide evidence for a task without gaining authority to direct that system. OWASP’s excessive-agency guidance describes risks from unnecessary functionality, permissions and autonomy. A well-defined tool boundary limits those capabilities according to the actual job. It does not assume that every tool result is a trusted instruction or that a prompt telling the model to be careful is enough enforcement.
A simple example
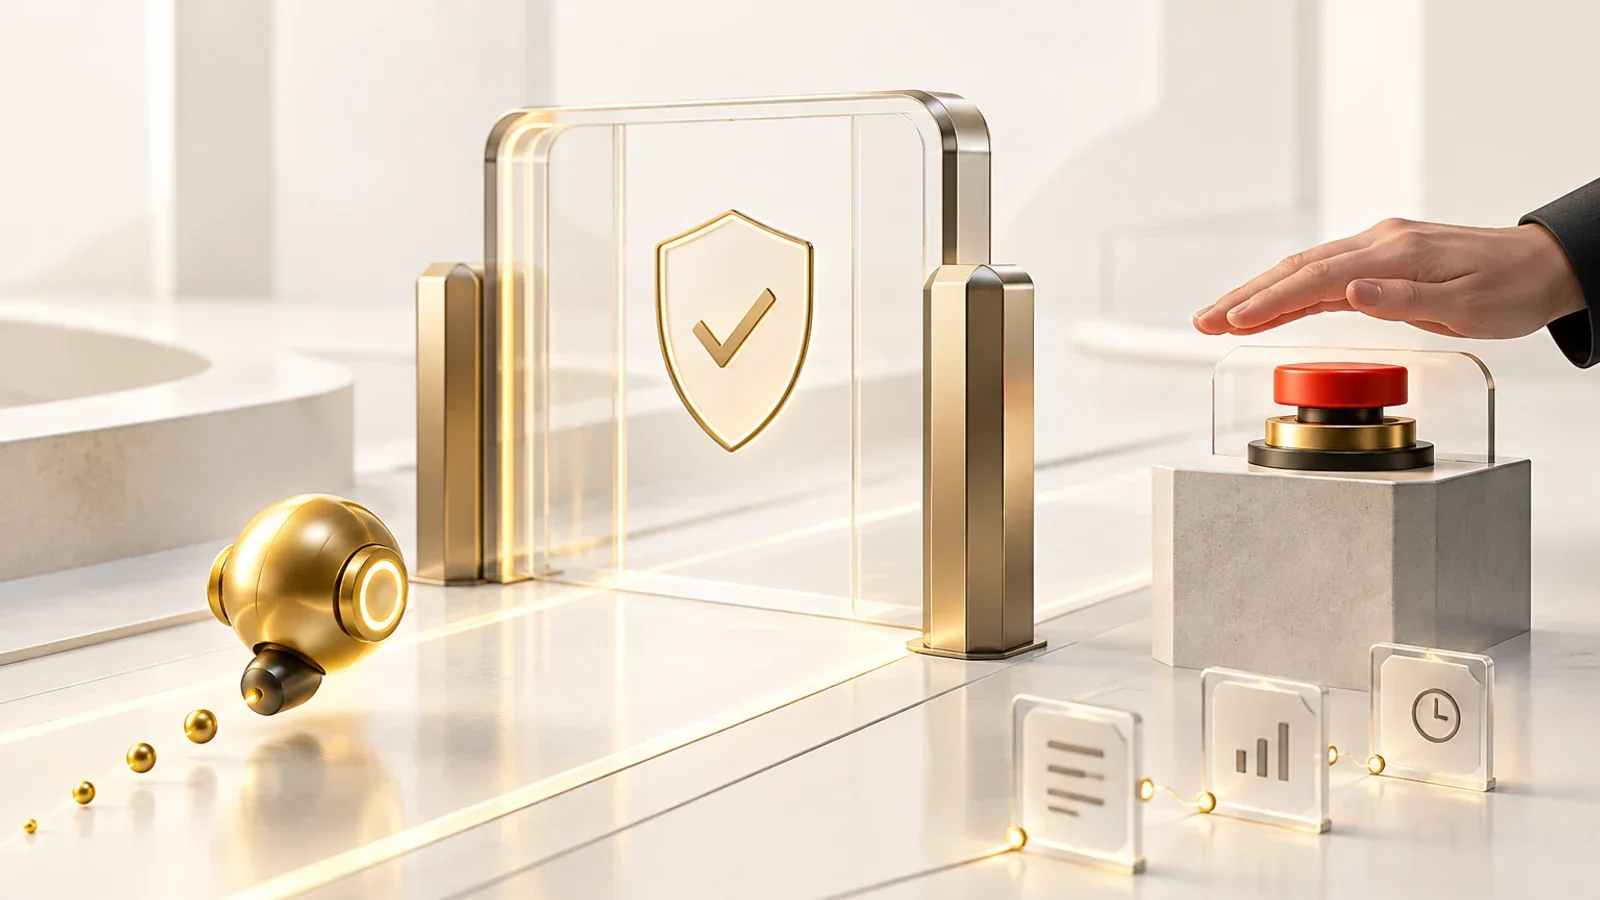
A research assistant can receive a read-only source lookup and a draft-writing function. Publishing the result is a different capability with a different consequence. If publishing is later authorized, the server should still check the reviewer, destination and exact action being executed. A tool called publish is not safe merely because its name appears on a list. The function needs its own resource and role checks, and the application needs useful failure and recovery behavior.
What to inspect
Ask where permission is enforced and what happens when the model requests an extra argument or an unrelated destination. Review the evidence needed for a consequential action and whether a retry can repeat it. A local allowlist example can illustrate request validation, but it cannot certify a production integration. The term helps a team discuss authority precisely: what the model can suggest, what the application can validate and what the authenticated user has actually authorized. Keeping those stages visible makes both useful automation and meaningful review easier.
References
- OWASP: excessive agency (living reference; accessed 2026-10-16)
Editorial note: AI-assisted original educational definition reviewed 16 October 2026. Examples and reading questions are BijliCoin explanation, not a product recommendation, legal conclusion or guarantee. AI-generated conceptual illustration.
Sources & context
See our editorial policy or report a correction.
Related guides and definitions
- Build an agent evaluation scorecard around accepted outcomes
A practical method for comparing agent changes without confusing fluent output, tool success or benchmark rankings with useful work.
- Choose a bounded workflow before giving an agent open-ended control
A practical design guide for deciding what an AI system may choose, what code should enforce and where a person remains responsible.
Join the conversation.
Loading reader discussion…
Sign in to like this article or add a comment. Comments are reviewed before appearing publicly.
Open the sign-in link in this same browser. Your display name is public; your email is private. Reader sign-in does not subscribe you to the newsletter. See our privacy notice.
Signed in as