What to know
- The joint advisory was published onSeptember22.
- Authorities describe fake interviews and malicious coding assessments.
- Candidate and employer verification should be paired with isolated, limited-access environments.
The official warning
A joint cybersecurity advisory published on 22 September 2026 describes WaterPlum, also known as Contagious Interview, as a North Korea-linked threat group targeting IT professionals through fake job offers, interviews and malicious coding tasks. The advisory discusses credential, sensitive-information and cryptocurrency theft, along with risks involving fraudulent workers. Attribution in this article is explicitly to the issuing authorities. It is not a basis for treating a nationality, an accent or a remote-work arrangement as evidence that a person is malicious.
Recruitment is also a code-ingestion process
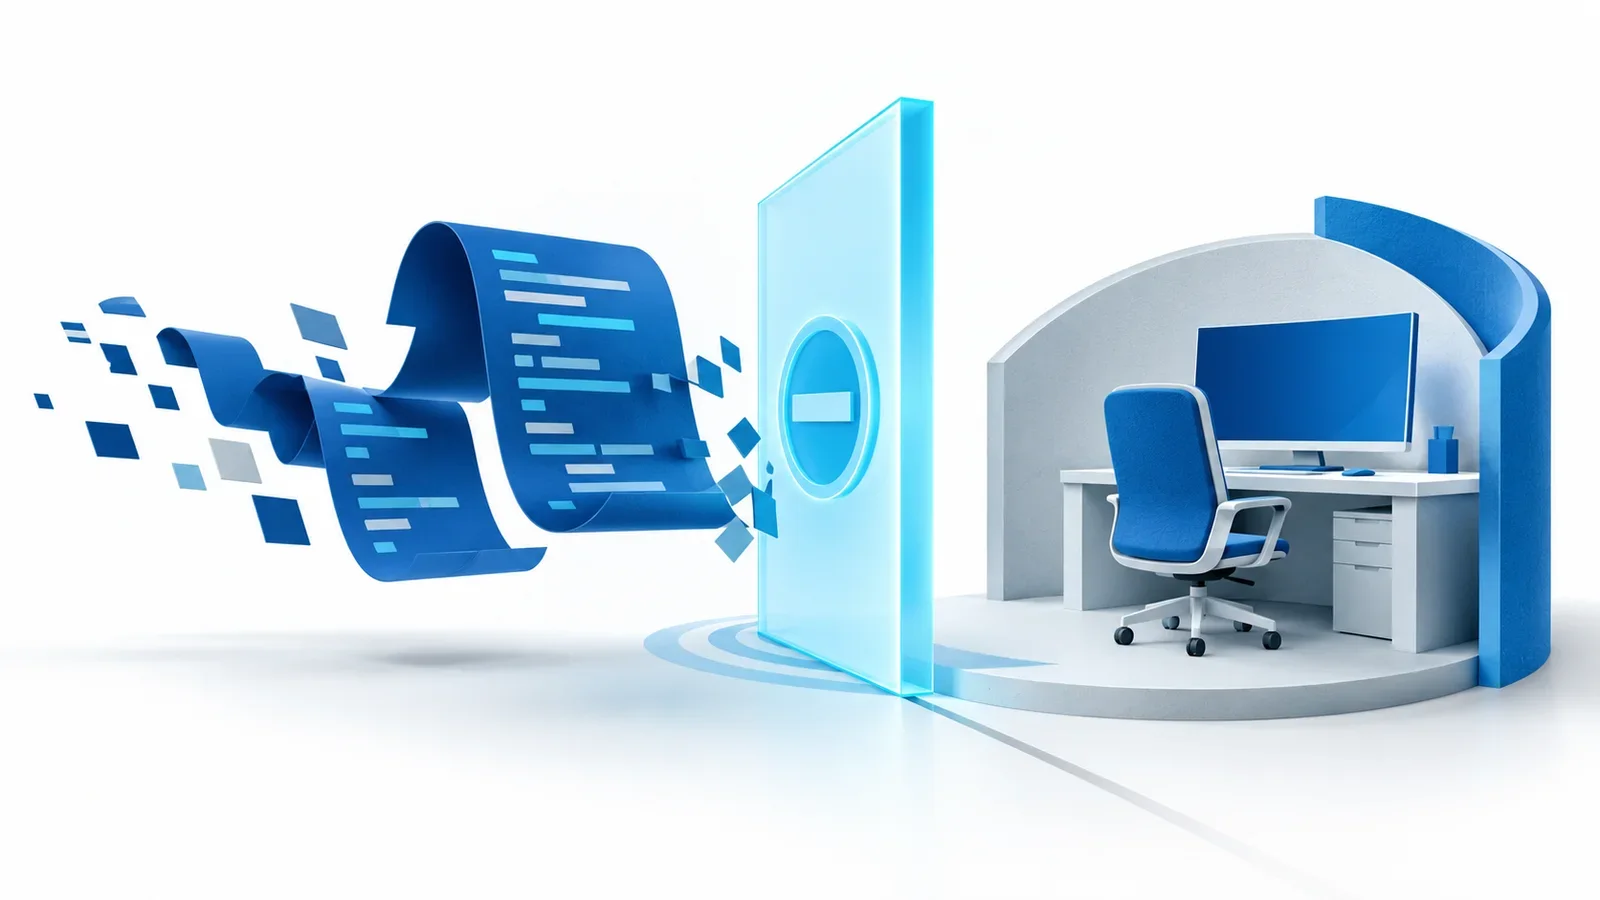
A technical assessment may ask an applicant to clone a repository, install dependencies or run a demonstration. Our interpretation is that this is a software-supply decision, even when the context feels like an ordinary conversation with a recruiter. The useful question is what the submitted code can access on the machine that runs it. A professional-looking organization name or a friendly video call does not answer that question. Verification and technical containment need to work together.
Separate evaluation from valuable access
A cautious developer can ask for a reviewable task description and confirm the company through an independently obtained channel. Unknown code should not inherit a browser session, production credentials, wallet files or an agent’s tool permissions simply because it is an assessment. Employers can make safer evaluation easier by using transparent tasks and avoiding unnecessary access requests. These are defensive editorial recommendations. This article does not provide instructions for executing suspicious samples or claim that a disposable container alone makes arbitrary code safe.
Employers have a second boundary to protect
Hiring controls should examine identity and work-history evidence consistently, with appropriate privacy and legal support. After hiring, access should match the work required and expand through an accountable process. Sensitive repositories, signing keys and production systems should not be bundled into a default developer account. A clear escalation path also helps legitimate applicants report a suspicious request without feeling that asking a security question will disqualify them. Good process protects candidates and organizations at the same time.
What to do with a suspicious approach
Preserve the messages and relevant identifiers without forwarding executable attachments broadly. If code was already run, involve the organization’s security team and follow its containment and credential-response process. A later clean scan does not necessarily establish that secrets were never accessed. The official advisory supplies the current campaign context; the response to a real machine needs its own evidence. The central lesson is to treat recruitment artifacts as untrusted input and keep them outside systems that hold valuable authority.
Sources and reading
- Joint WaterPlum recruitment threat advisory (2026-09-22)
Editorial note: AI-assisted original BijliCoin synthesis. Original BijliCoin synthesis of the linked public primary source. Defensive recommendations are editorial interpretation, not a claim of hands-on testing. No exploit procedure is provided. Illustration is conceptual.
Sources & context
See our editorial policy or report a correction.